How to Block VPN and Data Center IP Submissions in Spectra Forms
Co-founder & Brand Designer
Reviewed by Onar Alili
Anti-Abuse Engineer & Co-founder
Published 8 min read
Spectra has no setting to block VPN or data center IP addresses. The fastest fix is the oopspam Anti-Spam plugin (that’s us 👋). Install it, turn on Spectra protection, then enable Block Cloud Providers and, if needed, Block VPNs in the IP Filtering tab. This covers both the Form block and the Spectra Pro Register block. For a manual, network-level option, create Cloudflare custom rules that block hosting provider ASNs and Tor traffic.
Why VPN and Data Center IPs Are a Problem for Spectra Forms
Spectra powers contact and lead forms with its Form block, and user sign-ups with the Spectra Pro Register block. Bots that hit them fill your inbox with junk and your user list with fake accounts.
Most automated abuse comes from two sources:
- Data centers and cloud providers. Bots run on servers at AWS, Google Cloud, DigitalOcean, Hetzner and similar hosts. Real people rarely fill out a contact form or sign up from a server.
- VPNs and proxies. Spammers use them to hide their location and switch IP addresses between attempts.
Spectra doesn’t check where a submission comes from. Blocking by IP origin closes that gap, even for a bot with a fresh IP and no spam history.
Not sure where a suspicious IP comes from? Paste it into IP Reputation Check to see if it belongs to a VPN or data center.
Method 1: Block VPN and Cloud IPs with oopspam
The oopspam Anti-Spam plugin supports Spectra Forms and Spectra Pro Register natively. It checks every submission on the server before Spectra processes it. There is no CAPTCHA and no change to your forms.
Step 1: Install the Plugin
In WordPress, go to Plugins > Add New, search for oopspam Anti-Spam, then install and activate it.
Step 2: Add Your API Key
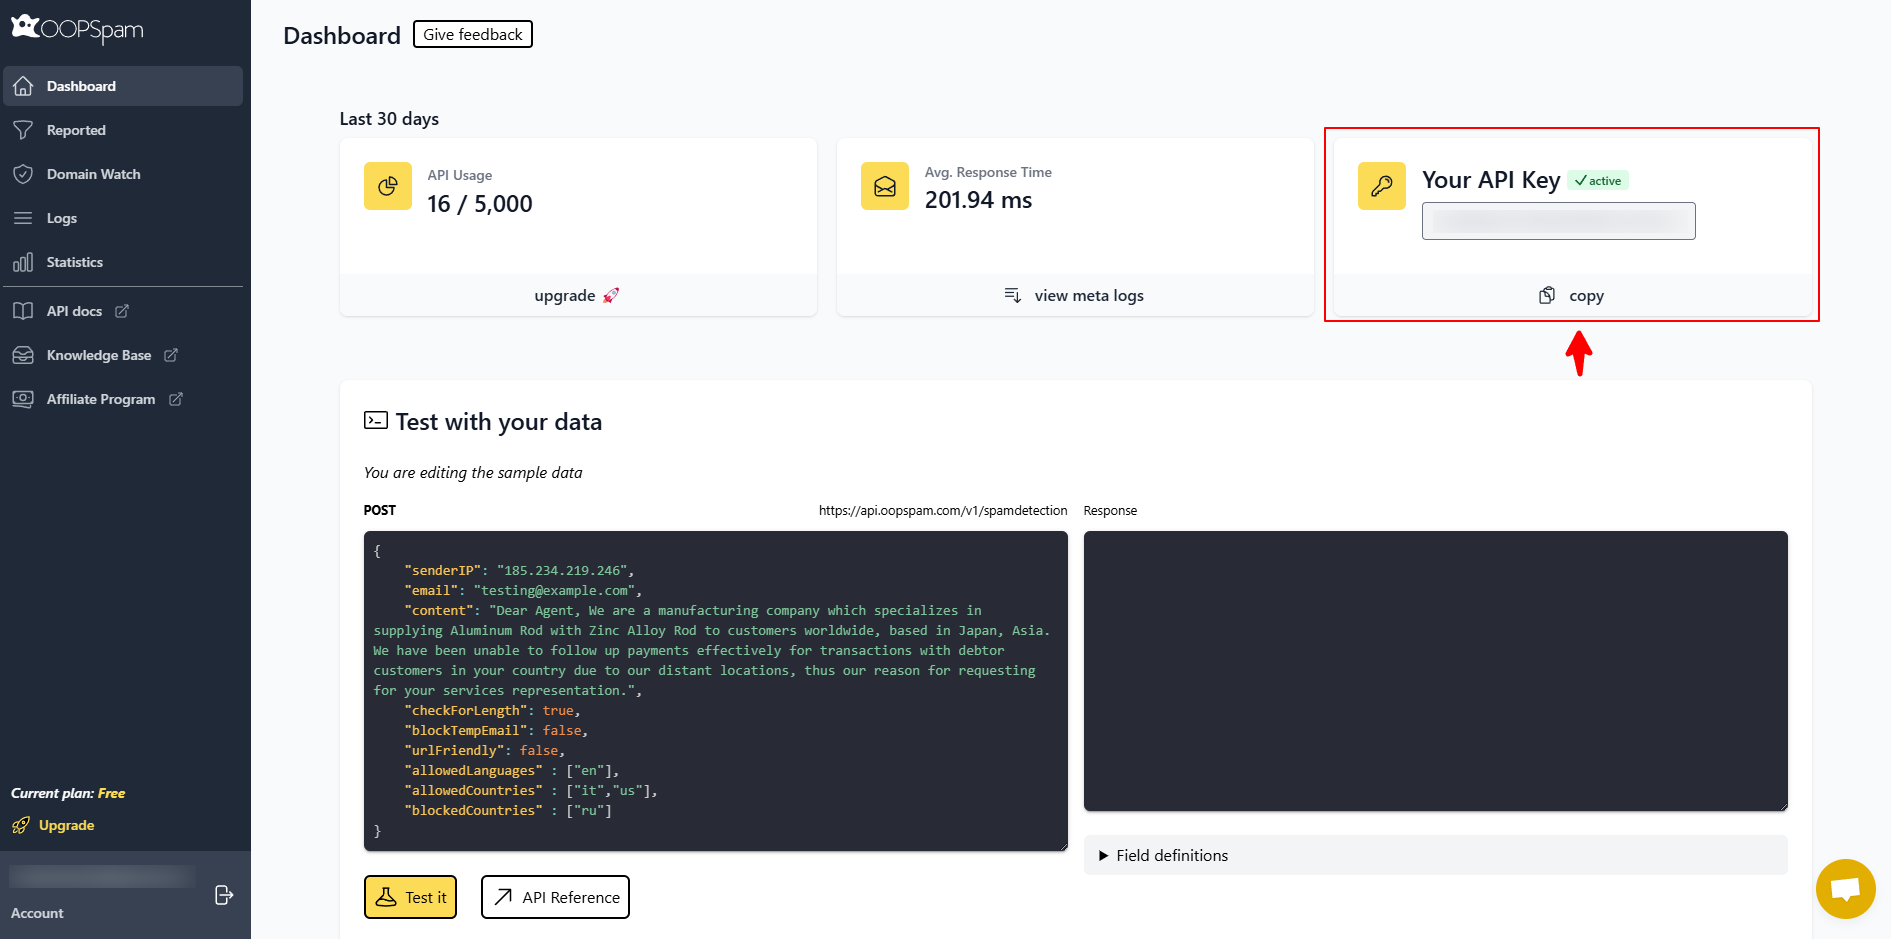
Create a free oopspam account and copy your API key. In WordPress, go to Settings > oopspam Anti-Spam. In the General tab, select oopspam Dashboard as the source and paste your key into My API Key.
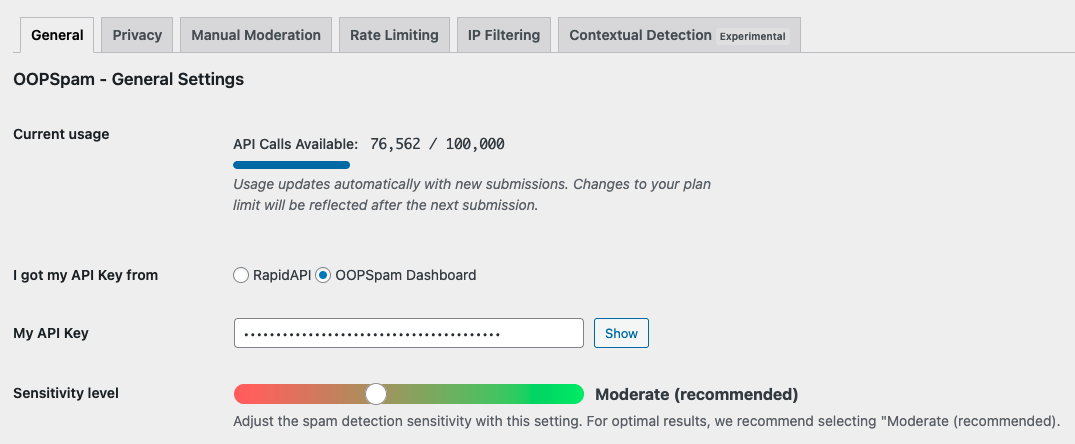
Step 3: Activate Spectra Protection
Scroll to the Spectra Forms and Spectra Pro Register section and turn on Activate Spam Protection. This covers every Form block and Register block on your site.
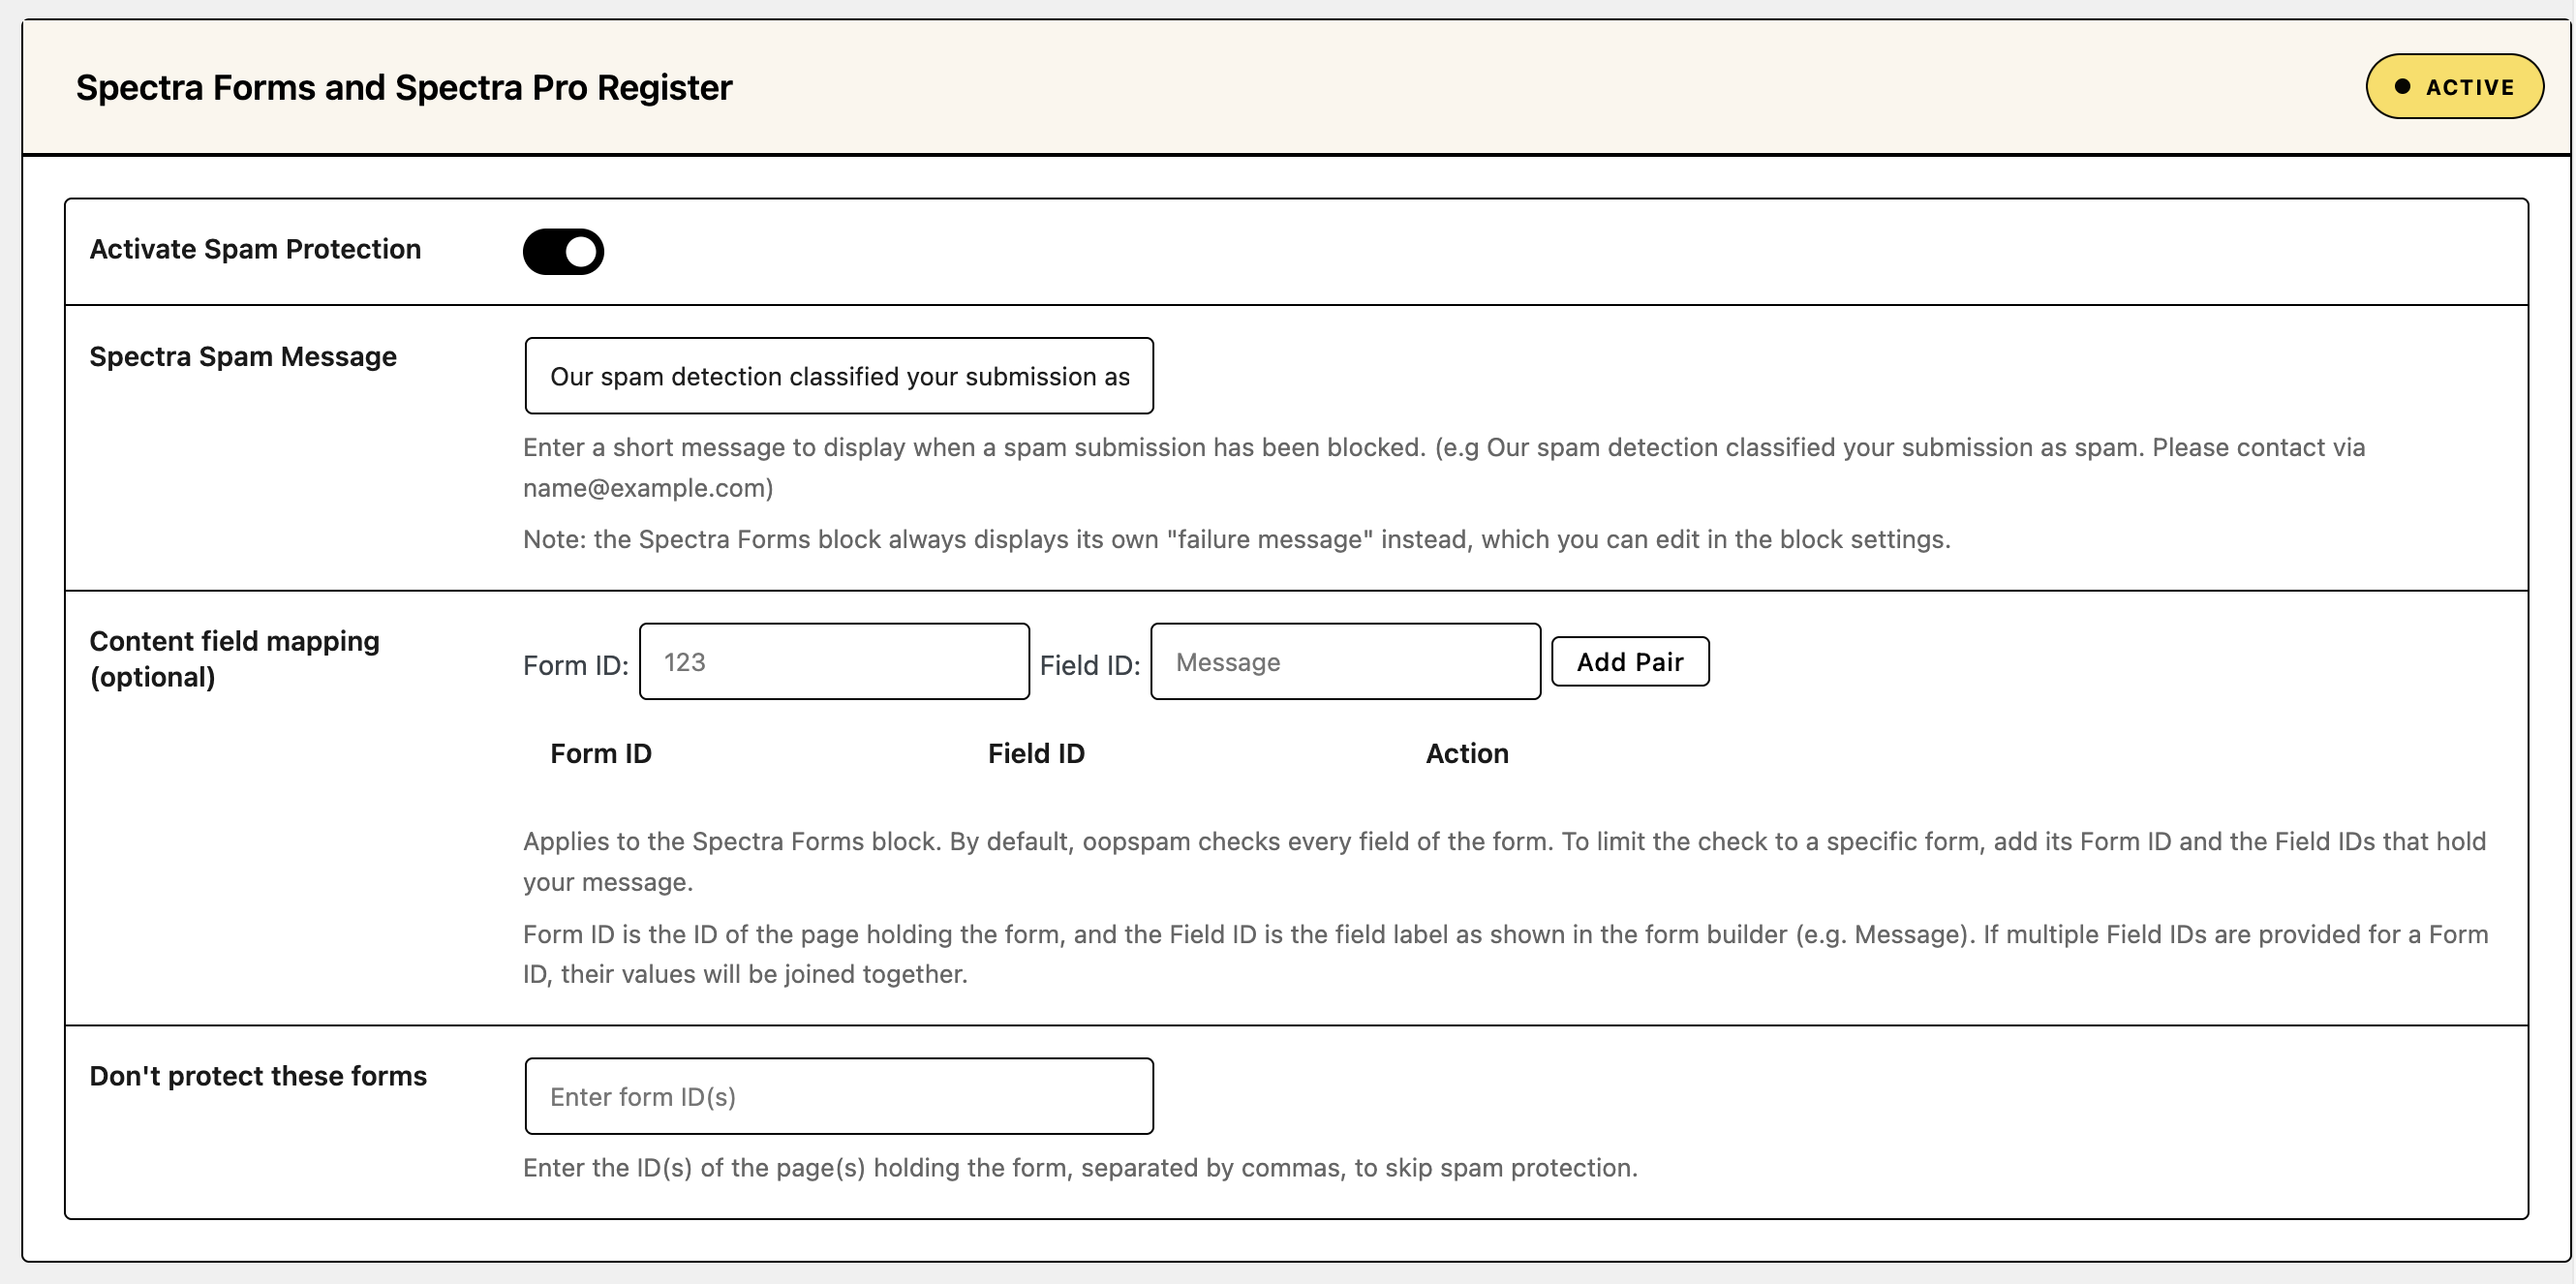
Step 4: Enable IP Filtering
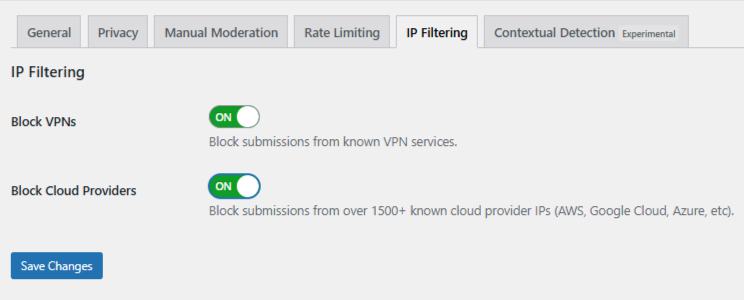
Open the IP Filtering tab. You’ll see two toggles:
- Block Cloud Providers: blocks submissions from 1,500+ known cloud providers, such as AWS, Google Cloud and Azure. This is the safer, high-impact setting. Turn it on first.
- Block VPNs: blocks submissions from known VPN services. Use it with care, because some real visitors use a personal VPN for privacy.
Click Save Changes.
Step 5: Turn On Trust Proxy Headers (If You Use Cloudflare or Another Proxy)
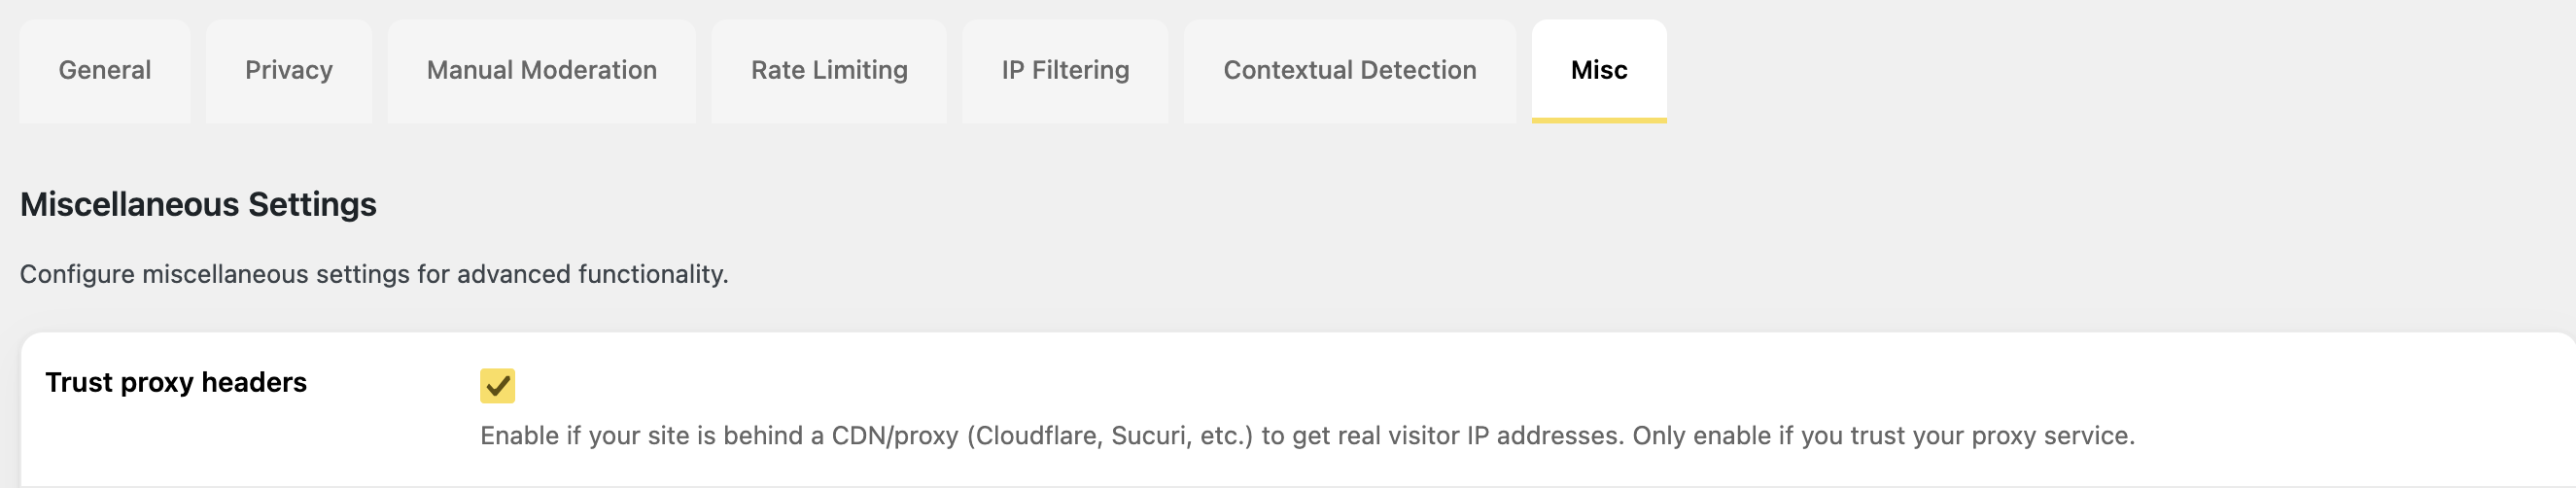
IP filtering only works if oopspam sees the visitor’s real IP address. If your site runs behind Cloudflare or another proxy, open the Misc tab and turn on Trust proxy headers.
Step 6: Set the Failure Message and Test
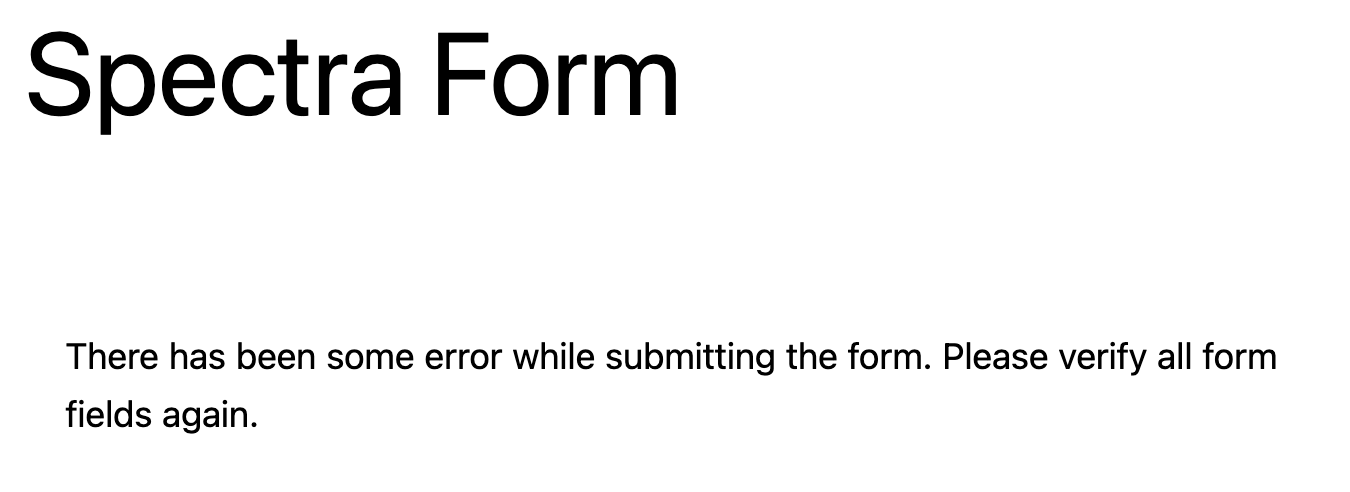
The Spectra Form block shows its own failure message when oopspam blocks a submission. Select the Form block, open its General settings and edit the Error Message Text, for example: “We couldn’t send your message. If you’re using a VPN, turn it off and try again, or email us at [email protected].”
The Register block shows oopspam’s Spectra Spam Message instead, so set that too, for example: “Please turn off your VPN and try again, or email us to create an account.”
Then connect to a VPN and submit the form. You’ll see the failure message instead of a success message.
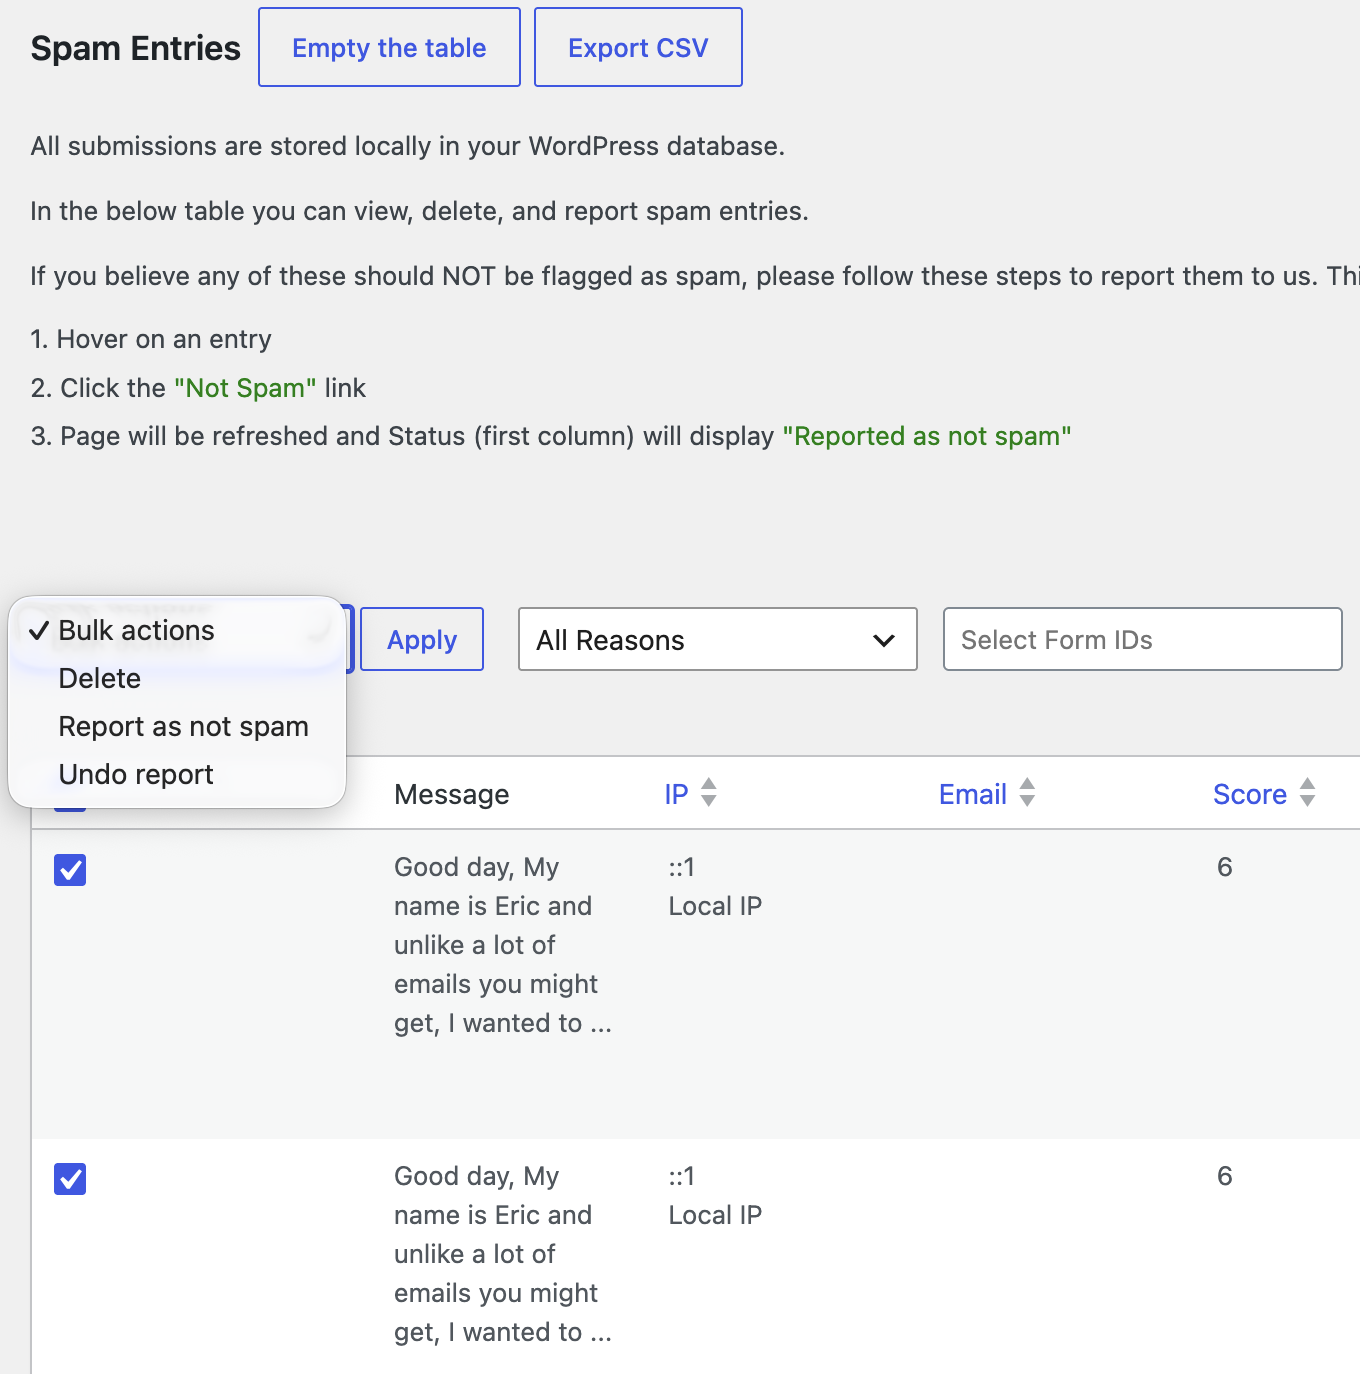
Open Form Spam Entries in WordPress. The entry should show VPN or cloud provider as the reason. If a real visitor was blocked, mark the entry as not spam. Learn more in the form entries guide.
Step 7: Add Extra Layers (Optional)
- Rate limiting: cap submissions per IP or email per hour.
- Country filtering: reject submissions from countries you don’t serve. See How to block countries in Spectra Forms.
Method 2: Block VPN and Cloud IPs with Cloudflare
If your site runs behind Cloudflare, you can block traffic at the network edge with custom rules that target ASNs (Autonomous System Numbers). An ASN identifies the network that owns an IP range, such as a cloud host.
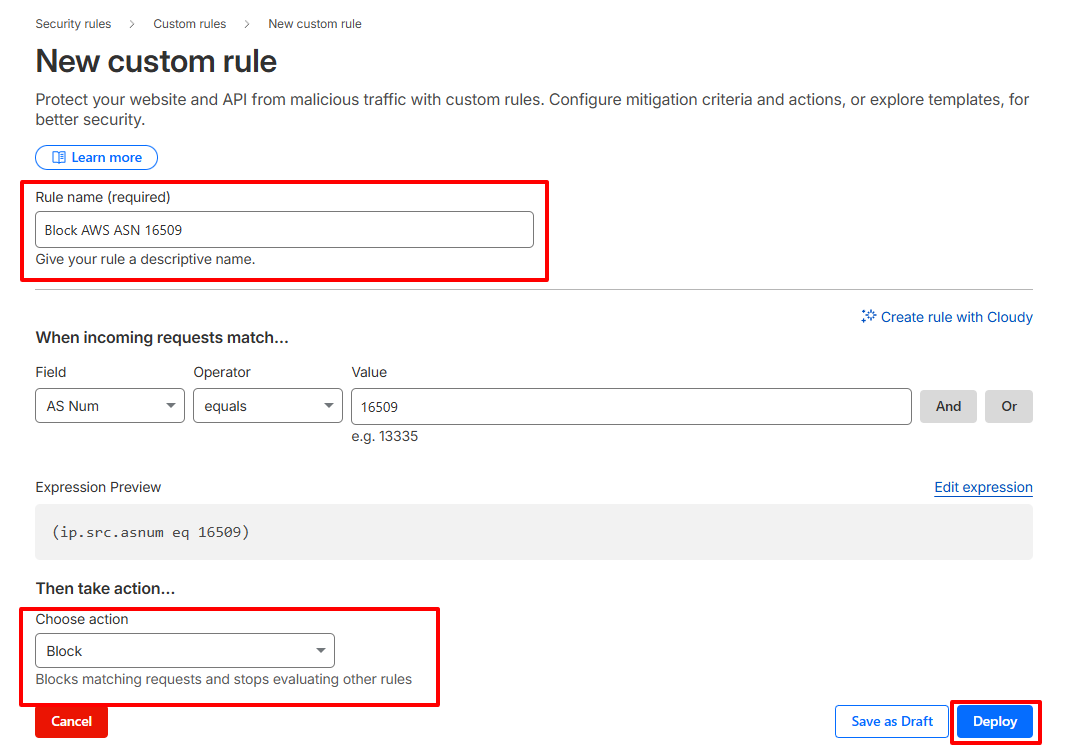
- In the Cloudflare dashboard, go to Security > Security Rules.
- Click Create rule, then select Custom rules.
- Name the rule, for example “Block hosting providers.”
-
Click Edit expression and add the ASNs you want to block:
 (ip.src.asnum in {14061 16509 14618 396982 63949 24940 16276 20473})
 or (ip.src.country eq "T1")
This covers DigitalOcean (14061), AWS (16509, 14618), Google Cloud (396982), Linode/Akamai (63949), Hetzner (24940), OVH (16276) and Vultr (20473). T1 is Cloudflare’s label for Tor traffic.
- Choose Block, then click Deploy.
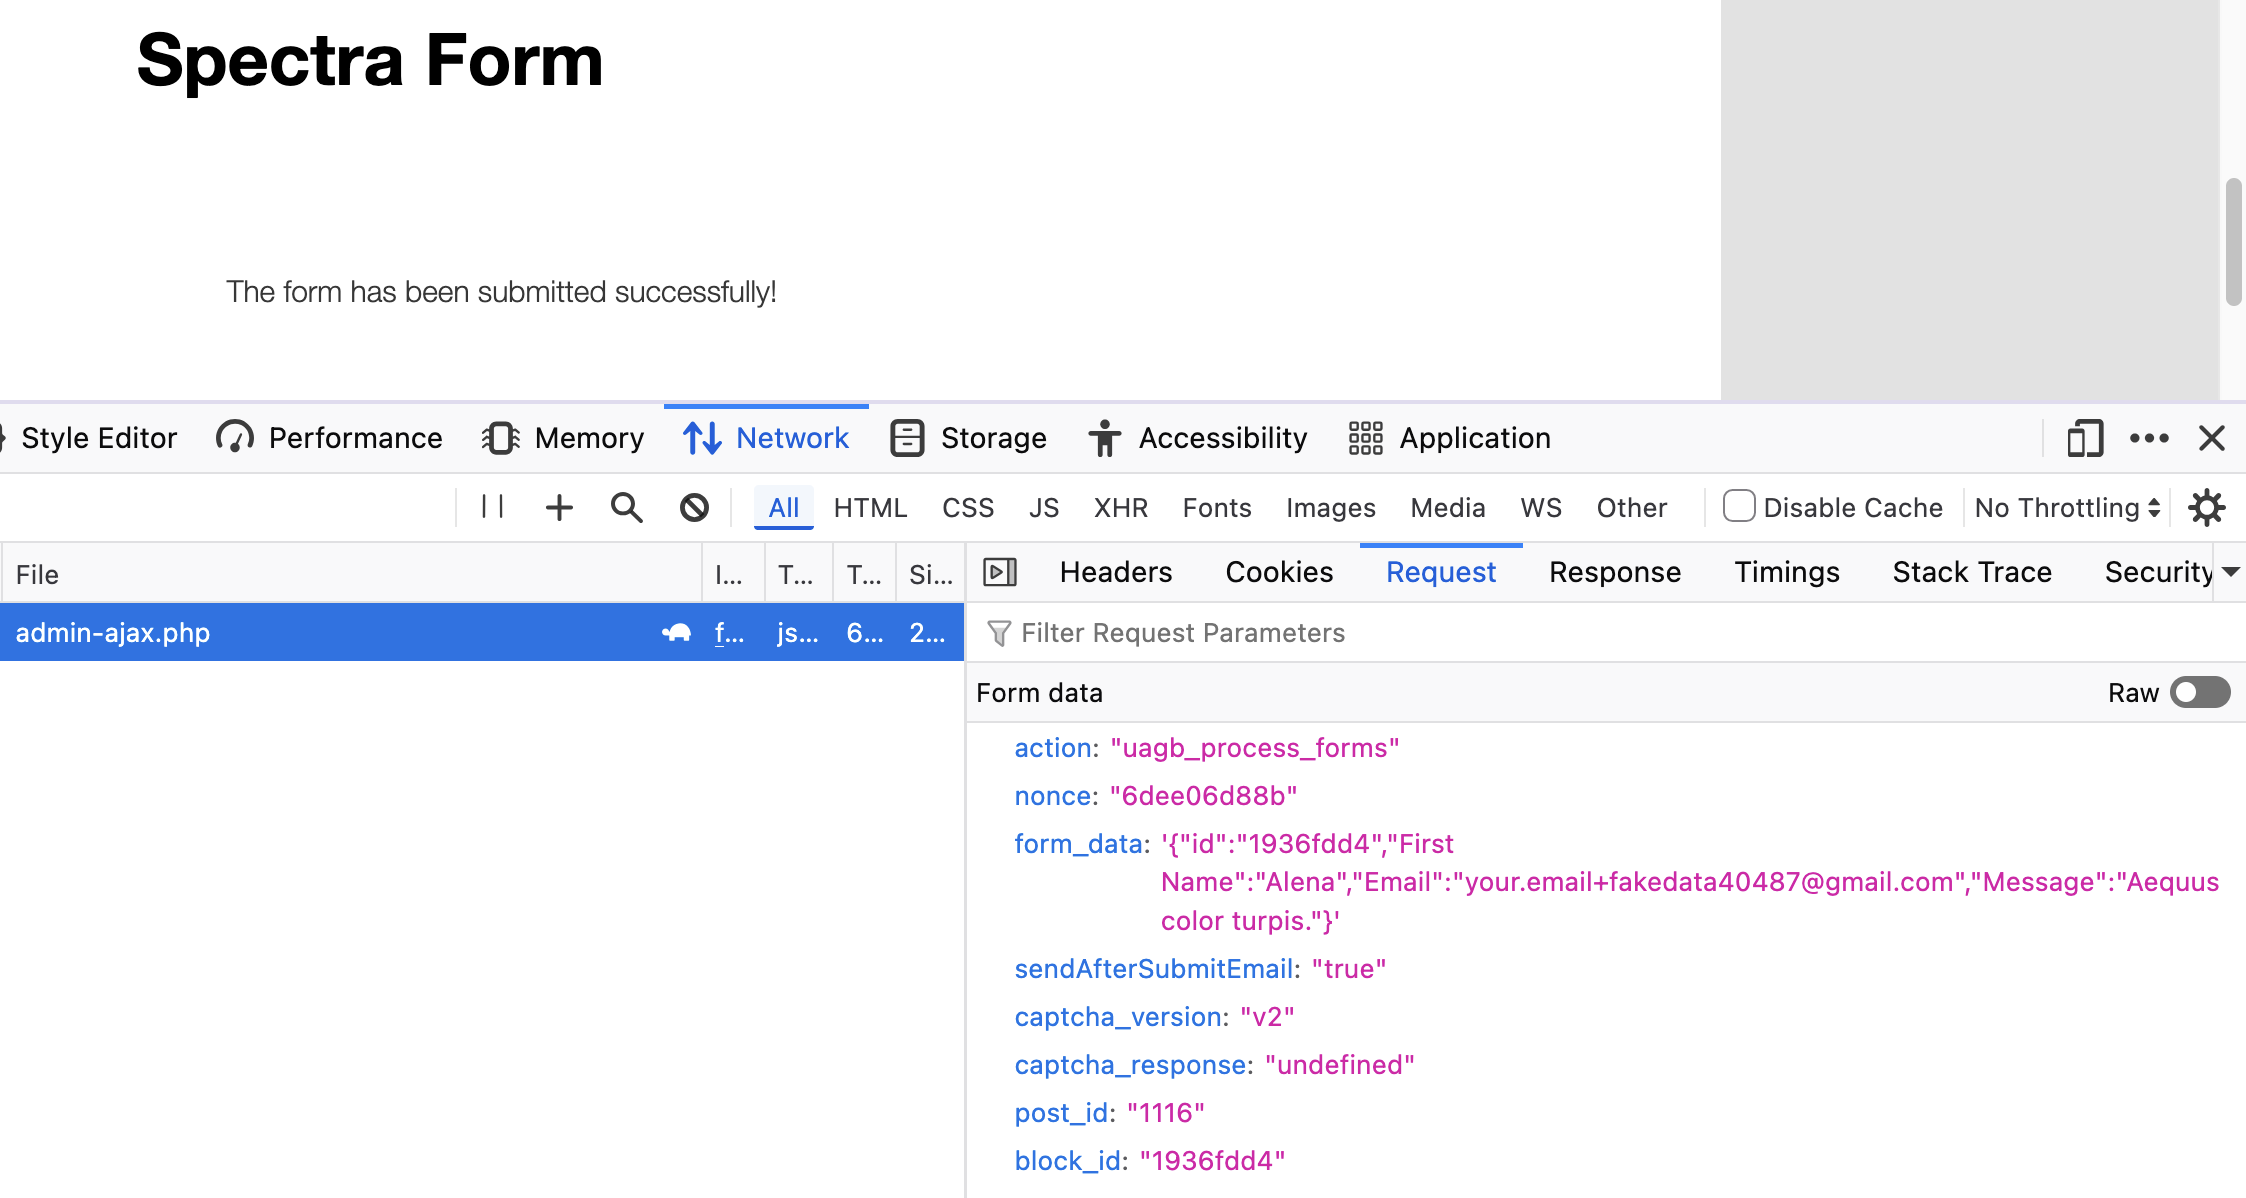
This rule applies to your whole site. Both Spectra blocks send submissions to WordPress’s shared AJAX endpoint, /wp-admin/admin-ajax.php: the Form block with the action uagb_process_forms and the Register block with spectra_pro_block_register. To scope the rule to that endpoint, wrap the conditions in parentheses and add the path:
((ip.src.asnum in {14061 16509 14618 396982 63949 24940 16276 20473})
or (ip.src.country eq "T1"))
and http.request.uri.path eq "/wp-admin/admin-ajax.php"
Three things to know:
- Other plugins use the same endpoint. The rule also blocks their AJAX requests from those networks, such as live search or cart updates. That’s rarely a problem for hosting providers, but test your site after deploying.
- Cloudflare can’t target one form action. The action name travels in the request body, which custom rules don’t read.
- Use Block, not Managed Challenge. AJAX requests can’t display a challenge page, so a challenged submission simply fails.
Limitations
- Manual upkeep. Hosting networks change, so you must update ASNs yourself.
- No commercial VPN coverage. Most VPN providers rent space across many networks.
- Rule limits. Cloudflare’s Free plan allows only five custom rules.
- False positives. Some legitimate businesses route traffic through cloud servers.
Cloudflare works best alongside oopspam, not instead of it. See Cloudflare’s custom rules documentation for more options.
oopspam vs Cloudflare: Quick Comparison
| oopspam | Cloudflare | |
|---|---|---|
| Setup time | About 5 minutes | 15 to 30 minutes |
| Maintenance | Automatic | Manual ASN updates |
| VPN detection | Yes | Tor only (T1) |
| Data center blocking | Yes, 1,500+ cloud providers | Only ASNs you add |
| Scope | Spectra forms and sign-ups only | Whole site, or all of admin-ajax.php |
| Logs with block reason | Yes, in WordPress | Cloudflare security events |
FAQ
Does Spectra block VPNs on its own?
No. Spectra doesn’t check whether a submission comes from a VPN or data center. Use oopspam or Cloudflare for that.
Does IP filtering protect the Register block too?
Yes. Once Activate Spam Protection is on, oopspam’s IP filtering applies to the Form block and the Spectra Pro Register block. That stops many fake sign-ups, which usually come from cloud servers.
Will blocking VPNs stop real visitors?
It can. Some people use a VPN for privacy or work. Start with Block Cloud Providers, add Block VPNs only if spam continues, and review your logs for false positives.
Does IP filtering work if my site uses Cloudflare?
Yes, as long as you turn on Trust proxy headers in oopspam’s Misc tab. Otherwise oopspam sees Cloudflare’s IP address instead of the visitor’s.
Final Thoughts
Bots that spam Spectra forms and create fake accounts mostly run on cloud servers and VPNs. oopspam blocks both with two toggles and no rule upkeep. Cloudflare adds a network-level layer for technical teams. Use one, or both for full coverage.
